Route 53
The domain registrar delegates DNS to the hosted zone’s nameservers. An alias record points the website domain to its CloudFront distribution.
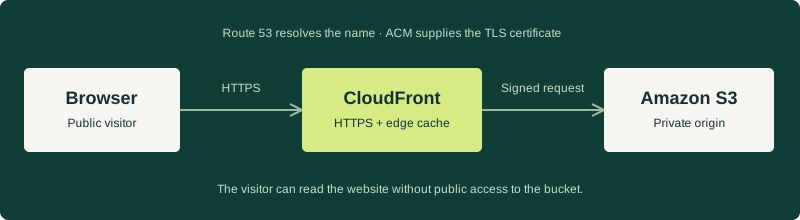
Each service has a specific job. Together, they connect a memorable domain to files stored behind a controlled origin boundary.
The domain registrar delegates DNS to the hosted zone’s nameservers. An alias record points the website domain to its CloudFront distribution.
A certificate proves the server is authorized to serve the requested domain and supports an encrypted TLS connection. CloudFront uses an ACM certificate in us-east-1.
The distribution receives the HTTPS request, serves a cached object when available, or fetches the file from S3. HTTP requests redirect to HTTPS.
The bucket stores HTML, CSS, JavaScript, and images. CloudFront uses the S3 REST endpoint with Origin Access Control, rather than a public S3 website endpoint.
Two different connections. The browser connects to CloudFront; CloudFront separately connects to S3. Origin Access Control signs that second request. It does not require the visitor to sign in.